
Policy and Procedure Management: Version, Approval and Acknowledgement
Learn how policy and procedure management connects version control, approvals, employee acknowledgement and audit evidence in one secure digital workflow.
Policy and Procedure Management: Creating a Controlled Document Lifecycle
Publishing a policy does not guarantee that employees can find the current version, understand what changed or confirm that they received it.
Documents often become fragmented across shared drives, email attachments, intranet pages and local copies. One location may follow the latest procedure while another continues working from an outdated PDF.
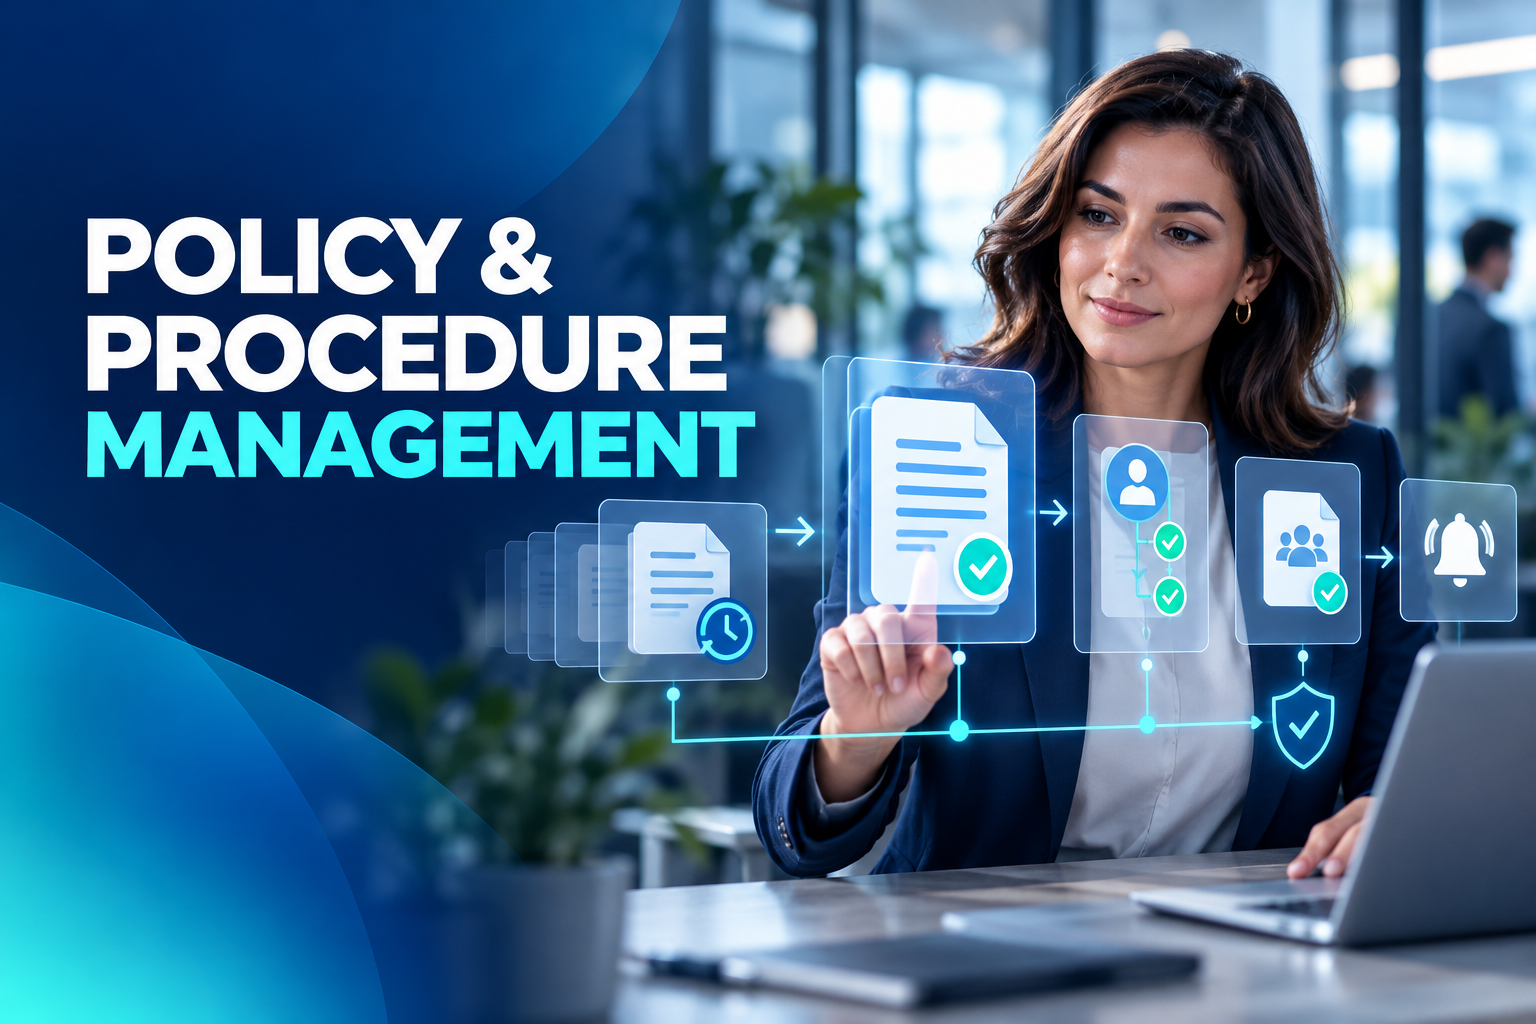
Policy and procedure management creates a controlled lifecycle from drafting and approval to distribution, acknowledgement, review and retirement.
What is policy and procedure management?
Policy and procedure management is the structured administration of workplace policies, operating procedures, instructions and standards through a central digital platform.
Unlike basic file storage, the platform connects each document with:
An owner
A category
A controlled version
An approval workflow
An effective date
A review date
A target audience
Access permissions
Employee acknowledgements
A complete activity history
The document becomes part of an operational process rather than an isolated attachment.
Common content categories include:
People and employment policies
Health and safety instructions
Information security standards
Codes of conduct
Travel and expense policies
Remote-working procedures
Quality and production instructions
Emergency procedures
Customer-service standards
Departmental operating guides
Organisations should distribute each document only to the populations that need it. Sending every policy to everyone can create notification fatigue and obscure important requirements.
Why shared folders do not provide governance
Employees cannot identify the authoritative version
Filenames such as “final,” “latest” and “approved” do not provide reliable version control. Copies downloaded to laptops or sent through email may remain in circulation after an update.
Approval decisions are fragmented
Comments and decisions can remain across email threads and meeting notes. Later, the organisation may be unable to establish who approved the content that entered force.
Distribution is confused with acknowledgement
An email delivery record does not prove that the recipient opened the policy, reviewed the correct version or completed an acknowledgement.
Review dates are missed
Policies can remain unchanged for years because their owners are not reminded to reassess them. Outdated documents then continue to guide operational decisions.
Audit preparation becomes a collection exercise
HR, quality and compliance teams may spend days retrieving current documents, approval records and signed lists from different departments.
How does a digital policy workflow work?
1. Create a central policy library
Existing Word and PDF files enter a controlled, searchable library. Each document receives an owner, category, audience and access classification.
Search should use meaningful metadata and document content, allowing an employee to find a procedure without remembering its exact filename.
2. Establish version control
The platform assigns a version and effective date. When an owner proposes a change, the existing record should not be overwritten. A new draft is created while the approved historical version remains available to authorised users.
The version history may show:
Previous and current content
Revision dates
Document owner
Change summary
Approval status
Effective date
Retirement date
This history helps the organisation answer which instructions applied at a particular point in time.
3. Route the draft for approval
The document follows a configurable review route. Depending on the subject, reviewers may include HR, legal, information security, quality, finance or local operational leaders.
Reviewers can approve, reject or request changes. Publication remains blocked until the required approvals are complete.
A multinational organisation may need a global policy with local appendices. The workflow should distinguish between central ownership and jurisdiction-specific review.
4. Publish to the appropriate audience
After approval, the platform distributes the document according to organisation, country, site, department, job family or position.
Employees receive access through mobile and web self-service. This is particularly important for frontline workers who may not have corporate email accounts or regular desktop access.
The employee should always see the currently effective version. Historical copies can remain restricted to administrators and authorised reviewers.
5. Capture acknowledgement evidence
The organisation can require different actions depending on the document:
View the document
Confirm receipt
Acknowledge reading
Answer knowledge questions
Complete related training
Apply an appropriate electronic-signature method
These actions are not legally or operationally identical. A click-to-acknowledge record should not be described as a qualified electronic signature unless it meets the applicable requirements.
The evidence may include employee identity, document version, delivery time, access time, acknowledgement time and reminder history.
6. Remind and escalate
Employees who do not complete the required action receive an automated reminder. If the deadline passes, the task can escalate to the line manager, HR or compliance owner.
Dashboards should identify exceptions by site, department and document rather than presenting only an organisation-wide completion percentage.
7. Schedule periodic reviews
Every controlled document should have an owner and review cycle. The platform sends a task before the review date.
The owner can confirm that the document remains current, revise it or retire it. A material revision can trigger new approvals, distribution and employee acknowledgement.
Policy, communication and training are different controls
A complete governance process distinguishes among three connected activities.
Policy management
The policy defines the approved rule, responsibility or standard. It requires ownership, version control and an effective date.
Employee communication
The announcement informs employees that the policy exists or has changed. Communication alone does not manage the underlying document.
Training and competence
Training helps employees understand and apply the required procedure. For a critical operational instruction, acknowledgement may not be sufficient. The organisation may also require a course, assessment or practical validation.
A connected platform can automatically assign training when a relevant procedure changes and report whether both acknowledgement and learning requirements are complete.
Building audit-ready evidence
A digital system can provide an authorised reviewer with a consolidated report showing:
Current approved policies
Document owners
Approval history
Version history
Effective and review dates
Assigned employee populations
Completed and missing acknowledgements
Reminder and escalation activity
Retired documents
Completion by entity, site or department
The existence of an acknowledgement does not prove that a procedure is being followed correctly in practice. Operational controls, training results and incident evidence should complement the document record.
Supporting multi-location and global organisations
A policy platform should allow central standards without removing local accountability.
The organisation may publish a global information-security policy while allowing country-specific privacy guidance. A hotel group may maintain one service standard while tracking acknowledgement separately at each property.
Important capabilities include:
Parent and local document relationships
Language variants
Local approval steps
Entity-specific effective dates
Restricted regional access
Consolidated and local reporting
Clear identification of the authoritative version
Translation should also be controlled. When the source document changes, the system should identify language versions requiring review.
Privacy and security requirements
Some policies contain confidential operating methods, security controls or commercially sensitive information. Access must reflect the document’s classification.
A policy management platform should support:
Role- and category-based permissions
Strong authentication
Controlled download and export
Version integrity
Access and acknowledgement logs
Removal of access for leavers
Retention and disposal rules
Secure backup and availability
Restricted external sharing
Segregation of administrator roles
External suppliers should receive only the procedures necessary for their work and should not gain general access to the employee document library.
Questions to ask during a software demonstration
Ask providers to demonstrate:
Bulk migration of existing documents
Metadata and full-text search
Draft, approved and retired statuses
Version comparison and history
Configurable approval routing
Audience selection by role and location
Mobile access for frontline employees
Acknowledgement and reminder tracking
Training assignment after a policy update
Country and language variants
Review-date notifications
Audit-ready reporting and exports
Permission and download controls
Handling of leavers and transfers
Use a scenario in which one procedure is updated after half of the workforce acknowledged the previous version. This reveals whether the system can identify who must review the new content.
Frequently asked questions
Can existing Word and PDF policies be migrated?
Yes. Existing documents can be uploaded, classified and assigned to owners. The organisation should verify which version is authoritative before publication.
Should employees acknowledge every new version?
That depends on the significance of the change and the organisation’s policy. A material update may require new distribution, acknowledgement or training.
Is an acknowledgement an electronic signature?
An authenticated acknowledgement can provide evidence of an action, but it is not automatically equivalent to an advanced, qualified or secure electronic signature.
Can policies be targeted by role or location?
Yes. Distribution can be limited by entity, site, department, position or another authorised employee group.
What happens when a review is overdue?
The system can remind the document owner, escalate the overdue task and report the document as requiring attention.
Turn policy documents into managed workflows
HR&Tomorrow’s Procedure module brings policies and instructions into a central library with version control, approval routing, targeted publication, employee acknowledgement and audit reporting. Policy changes can also trigger related learning or task workflows. HR&Tomorrow
Request an HR&Tomorrow demo to see how policy and procedure management can replace fragmented documents and signature lists with a controlled, searchable and auditable workflow.